Chinese Hackers Use AI-Powered ARTEX to Target Over 200 Organizations Worldwide.


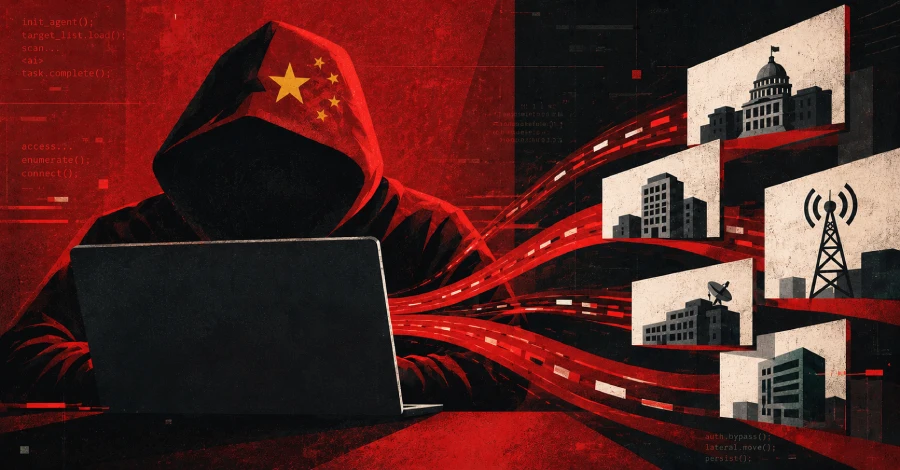
Chinese state-sponsored threat actors have been observed using a Go-based artificial intelligence (AI)-powered penetration testing framework called ARTEX in attacks aimed at high-value targets simultaneously.
The activity has been attributed by CrowdStrike to a China-based "targeted intrusion adversary" it tracks under the moniker Vapor Panda (previously VexatiousTemper). First identified in February 2021, the hacking group overlaps with a threat cluster detailed by Trend Micro as Earth Estries.
"Agentic tooling like ARTEX enables this scale of expansion at speed, allowing a small team to pursue a wider target set than manual operations would support, rather than a wholesale shift away from the adversary's established access-development mission," CrowdStrike said in a Thursday analysis.
Starting October 17, 2026, Vapor Panda is said to have used the AI tool against more than 200 distinct organizations across the world, including foreign ministries in Latin America, Europe, Asia, and the Middle East; semiconductor, defense, and think tank organizations in the U.S.; and telecommunications providers in multiple regions. https://tinyurl.com/4uhhsrrk